A compliance report for every control
Compliant, partially compliant, non-compliant, not applicable with a documented reason, or an active exception.
On the DFX Index platform we measure where your organisation stands in AI, information security or digital transformation, with a published, evidence-based methodology, and hand you a signed report and a prioritised plan.
Your organisation knows it needs AI and stronger security, but not exactly where it stands, how far it is from target, or where to begin. An investment decision needs measurement, not an impression.
The whole assessment runs on one platform: start with twenty free questions and an instant indicative result, then move to the full evidence-based assessment, at index.dfxkw.com
An annual self-assessment built on the National Essential Cybersecurity Controls, with a compliance report for every control, an action plan, and a record kept for three years.
The National Cyber Security Center issued Decision No. 2 of 2026 on the National Essential Cybersecurity Controls, published in the official gazette Kuwait Al-Youm on 5/4/2026. The decision sets 28 essential controls and 16 controls for cloud services, and gives organisations 18 months to comply, that is, until about 5/10/2027.
The decision requires every organisation to carry out a self-assessment at least once a year, documenting the results, the main gaps, the actions and the target dates, and to keep the record for at least three years.
DFX Index turns this obligation into a clear working cycle. Your team answers questions mapped to each control and attaches the evidence, and a colleague reviews it before approval. A DFX expert then reviews every item, so no score confirming implementation counts without acceptable evidence.
The result is a compliance report showing the status of each of the 44 controls, an action plan with an owner and a date for every gap, and an annual self-assessment record ready to export.
Compliant, partially compliant, non-compliant, not applicable with a documented reason, or an active exception.
No item is scored as implemented without acceptable evidence, so the report reflects reality, not intentions.
Every exception has its reason, compensating controls and expiry date, as control GOV-2 requires.
Every gap has an action, an owner and a target date before the deadline.
A single exportable document bringing together results, gaps, actions and dates, kept for at least three years.
The annual subscription includes an assessment now, a re-assessment after six months, and a progress report comparing the two.
For controls that need evidence from the systems themselves, such as multi-factor authentication, log retention and blocking public access in the cloud.
Every report in Arabic and English, each file with a fingerprint its recipient can verify.
A ready presentation built from the assessment results for the board.
Where your organisation stands among its sector peers without revealing any name, once the sector reaches five organisations.
Compares the second cycle with the first.
With Microsoft Entra accounts or any provider that supports OpenID Connect or SAML 2.0.
For deadlines and reviews, with each user's consent.
20 questions, a few minutes.
Ten weighted pillars, from strategy and governance to data, use cases and responsible AI.
Ten weighted pillars, from governance and risk to identity, monitoring, response and third-party security.
Ten weighted pillars, from digital strategy and governance to user experience, integration and data.
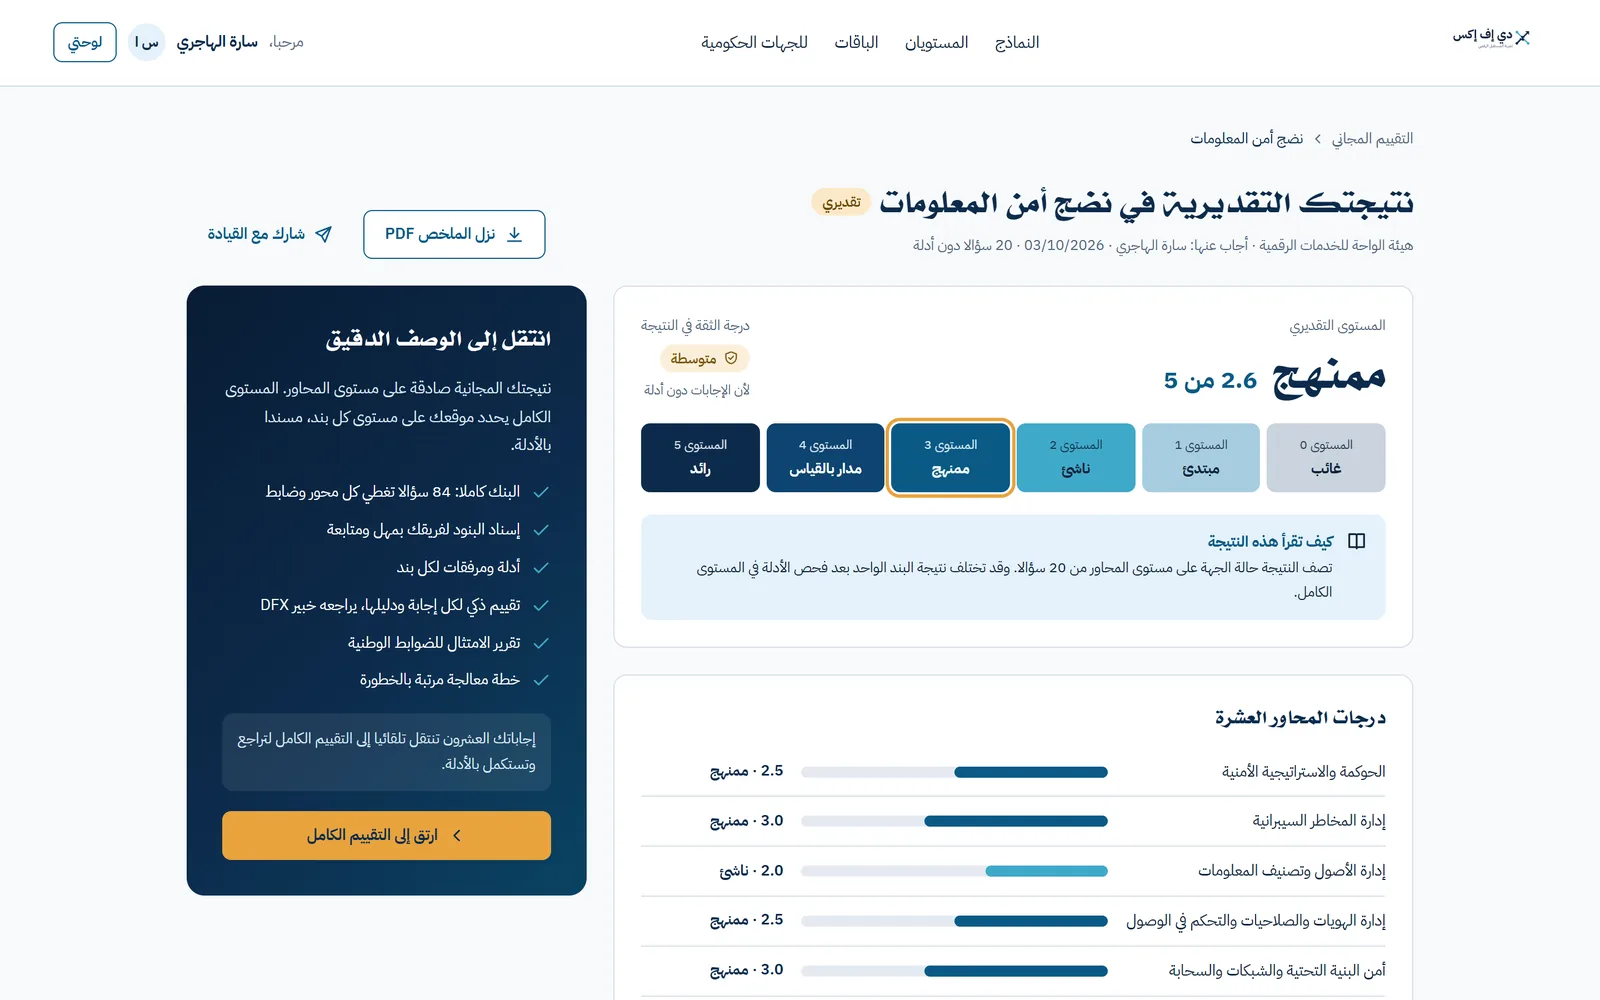
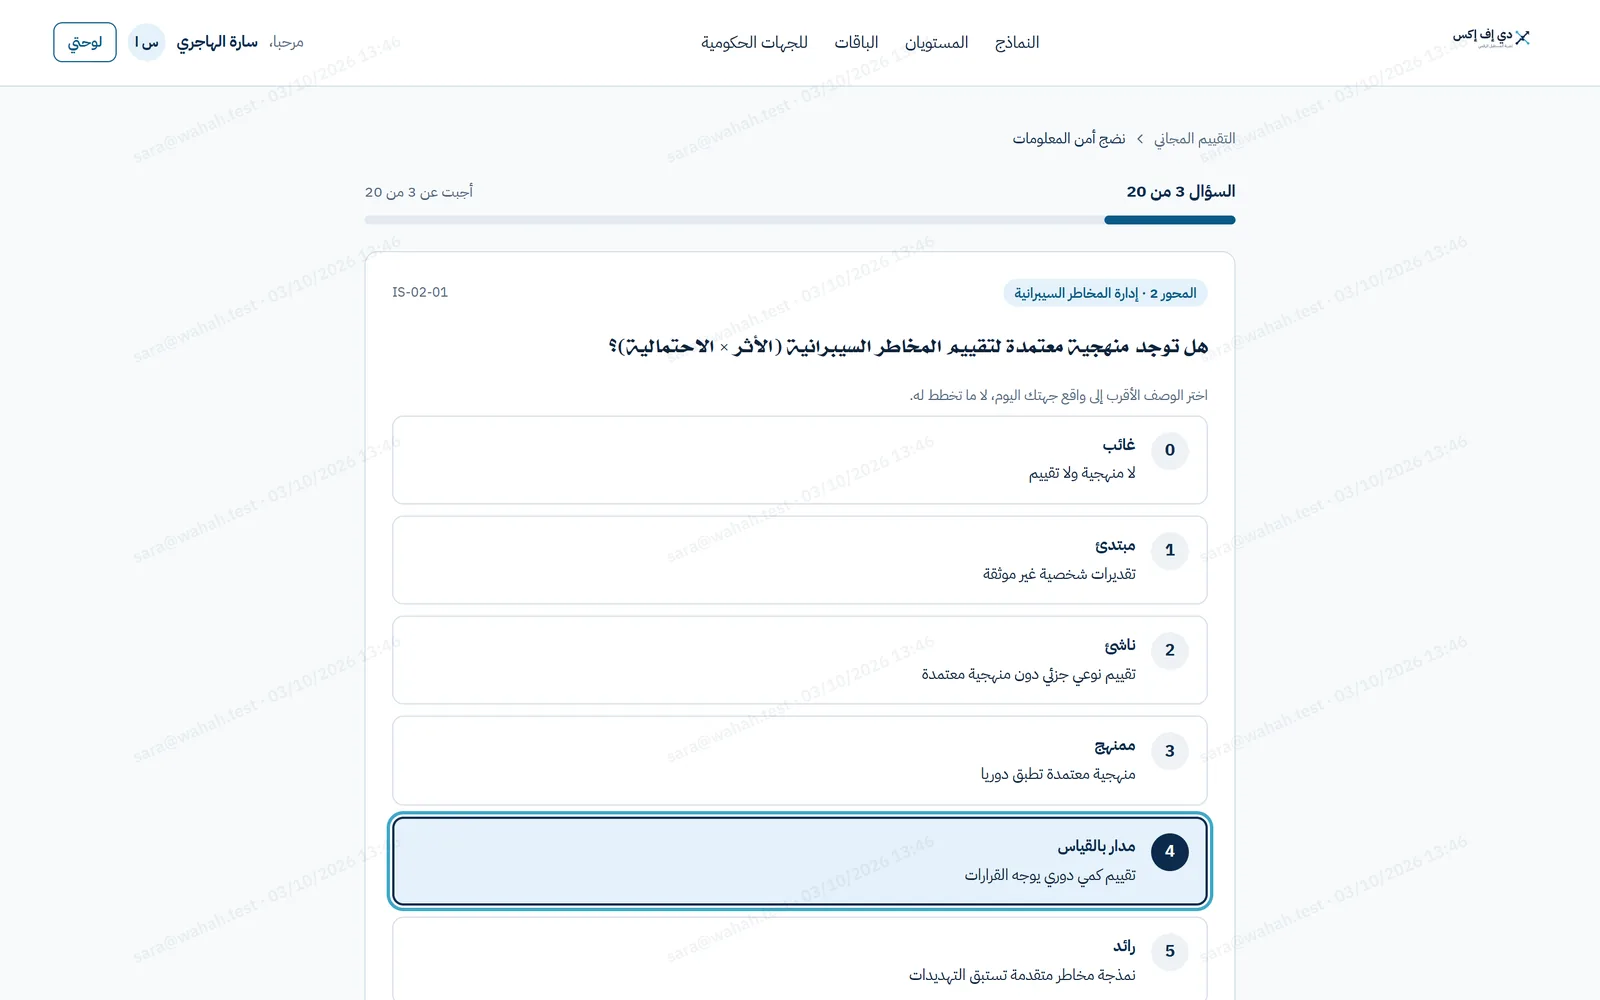
Twenty questions you answer in minutes, with an instant indicative result that shows your overall position.
Questions are assigned inside your organisation with deadlines, review and approval; evidence is attached and assessed by an AI engine, then reviewed by a DFX supervisor before any result.
You receive: A professional report signed with a verification fingerprint, an indicator dashboard, and a plan ordered by severity and priority.
| Organisation size | One model | All three models | Annual subscription |
|---|---|---|---|
| Small (under 50 employees) | 900 | 2,000 | 1,350 |
| Medium (50 to 250 employees) | 1,500 | 3,400 | 2,250 |
| Large (250+) or government | 2,500 | 5,600 | 3,750 |
Annual subscription: a full assessment of a model you choose, a re-assessment after six months at no extra cost, a progress report comparing both cycles, and a DFX expert review in each cycle.
Each answer is scored 0 to 5 and backed by evidence; a weighted formula places your organisation on this scale:
Twenty questions and an instant indicative result.
Your coordinator assigns questions to their owners, then reviews and approves the answers.
The AI engine assesses the evidence, and a DFX supervisor reviews every assessment before it is issued.
A report with a verification fingerprint anyone can check, and a prioritised plan.
Led by Eng. Yousef AlMazeedi, a certified Lead Implementer of ISO/IEC 27001 and ISO 22301, with over 20 years in information technology, including leading the IT and communications function at a regulatory authority from 2019 to 2026. About the founder
On request we send a sample report completed for a fictional organisation, so you know what you'll receive before you start.
Choose a track and we'll send the methodology and a sample report before you commit.
Request an assessmentWant to build what the assessment uncovered? Smart technology solutions