 RestaurantCore
 LegalCore
 CommunityCore
 MADAR
 DFX Index
 GRC
GRC
When the auditor asks for proof, you find it in minutes, not days. Policies, risks, controls, evidence and audits on one platform for information security governance and compliance.
A quick tour

Who is it designed for, and who is it not right for?
✓Right for
Banks, financial institutions, government bodies and listed companies, and any organisation that an auditor or regulator asks for evidence across more than one framework, or that is working towards ISO 27001. It is built for the information security officer, the governance team, the internal auditor and senior management.
–Not right for
Anyone who wants evidence pulled automatically from their cloud systems, or controls approved by AI. In GRC, each control owner uploads their own evidence, the system suggests mappings and drafts, and a person always approves.
The auditor asks for proof, and the team spends a week searching
- Controls live in an Excel file, and the evidence sits in the inbox of someone who has left.
- Every framework has its own spreadsheet, and the same evidence is gathered three times.
- The policy is approved, and nobody knows who has read it.
- The board report is put together by hand before every meeting.
Your compliance before GRC, and with it
| Area | Before GRC | With GRC |
|---|---|---|
| Frameworks | A spreadsheet for each framework | One unified control library mapped to every framework |
| Evidence | Gathered when the audit comes | One piece of evidence covers several requirements |
| Control status | Typed in by the control owner | Derived from the latest test and the most recent evidence |
| Board report | Prepared by hand before every meeting | Ready at any time |
Three steps and you're under way
Choose your frameworks
Pick the frameworks your organisation must follow, and enter your current controls.
Map once
Map each control once to the requirements of every framework, and set its owner and its evidence.
Track your compliance
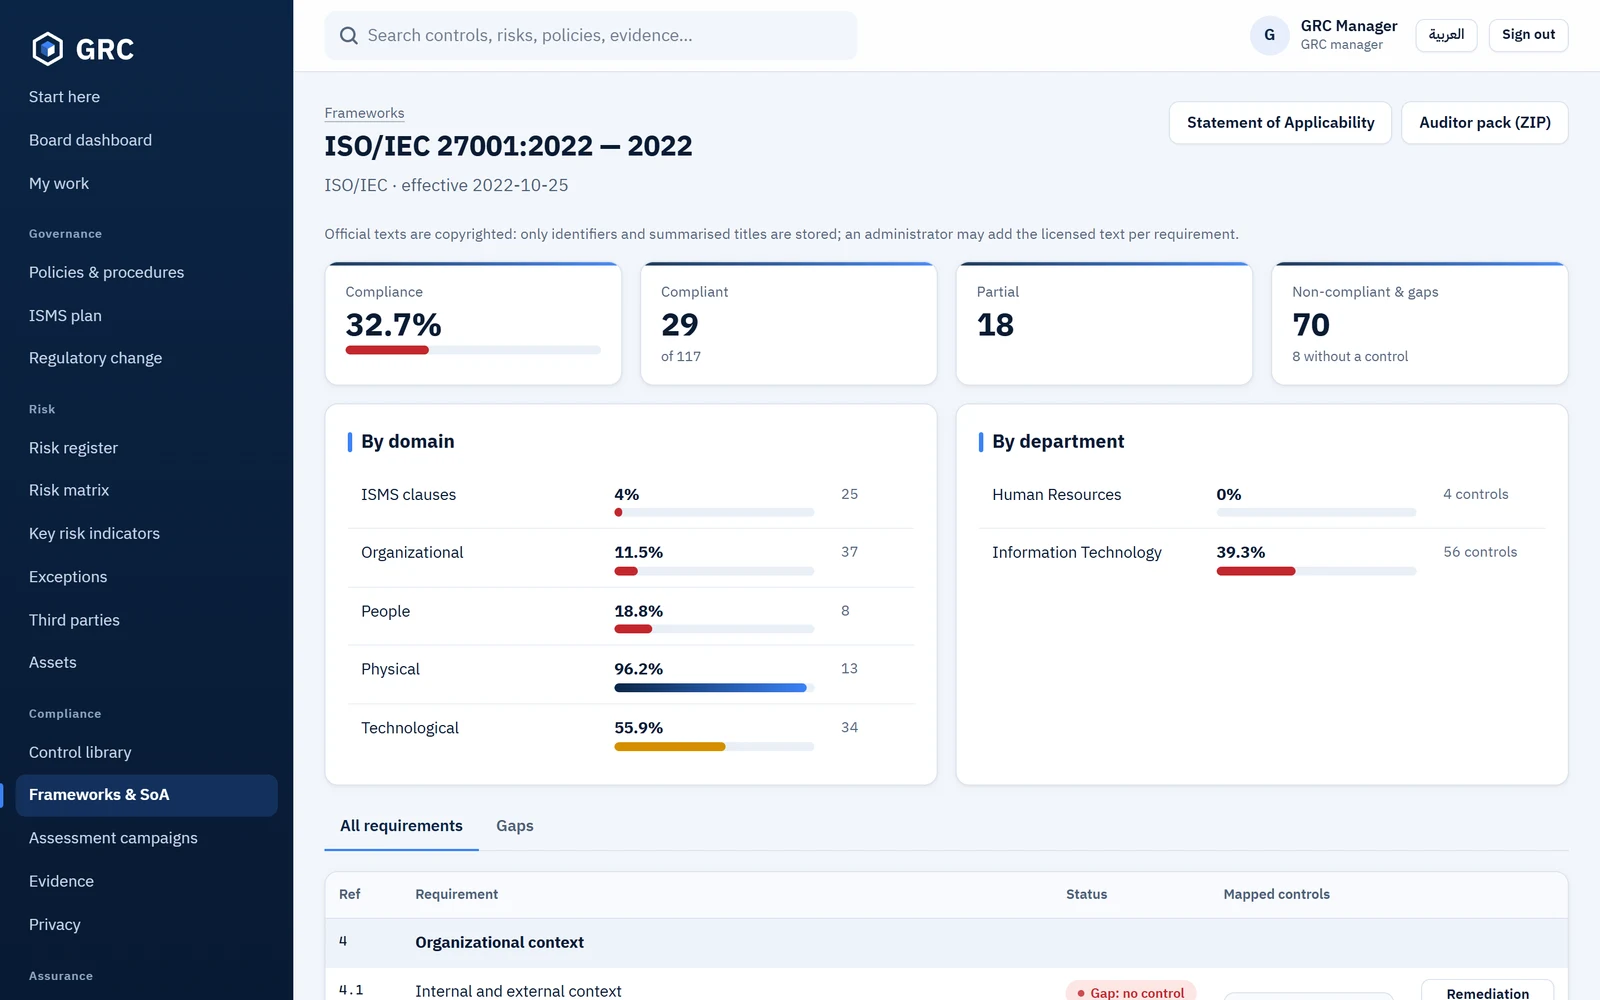
The system reminds owners about their evidence and calculates your compliance score for each framework, domain and department.
What it does
One unified control library
Map each control once to the requirements of every framework you follow, so one piece of evidence covers several requirements and every audit and compliance cycle takes less effort.
ISO 27001 and NIST CSF 2.0
Choose the frameworks your organisation must follow. We keep the ISO clause numbers and titles, and your organisation can upload its licensed text if it wishes.
Control status from the facts
Each control's status is derived from its latest test and most recent evidence, not from what its owner writes.
Reminders and compliance scores
The system reminds control owners about their evidence and calculates your compliance score for each framework, domain and department.
Evidence that cannot change
Every piece of evidence carries a fingerprint that cannot change after upload, with an audit trail of every view and approval.
Segregation of duties
Whoever creates a record cannot approve it: segregation of duties is built into the system.
A board dashboard
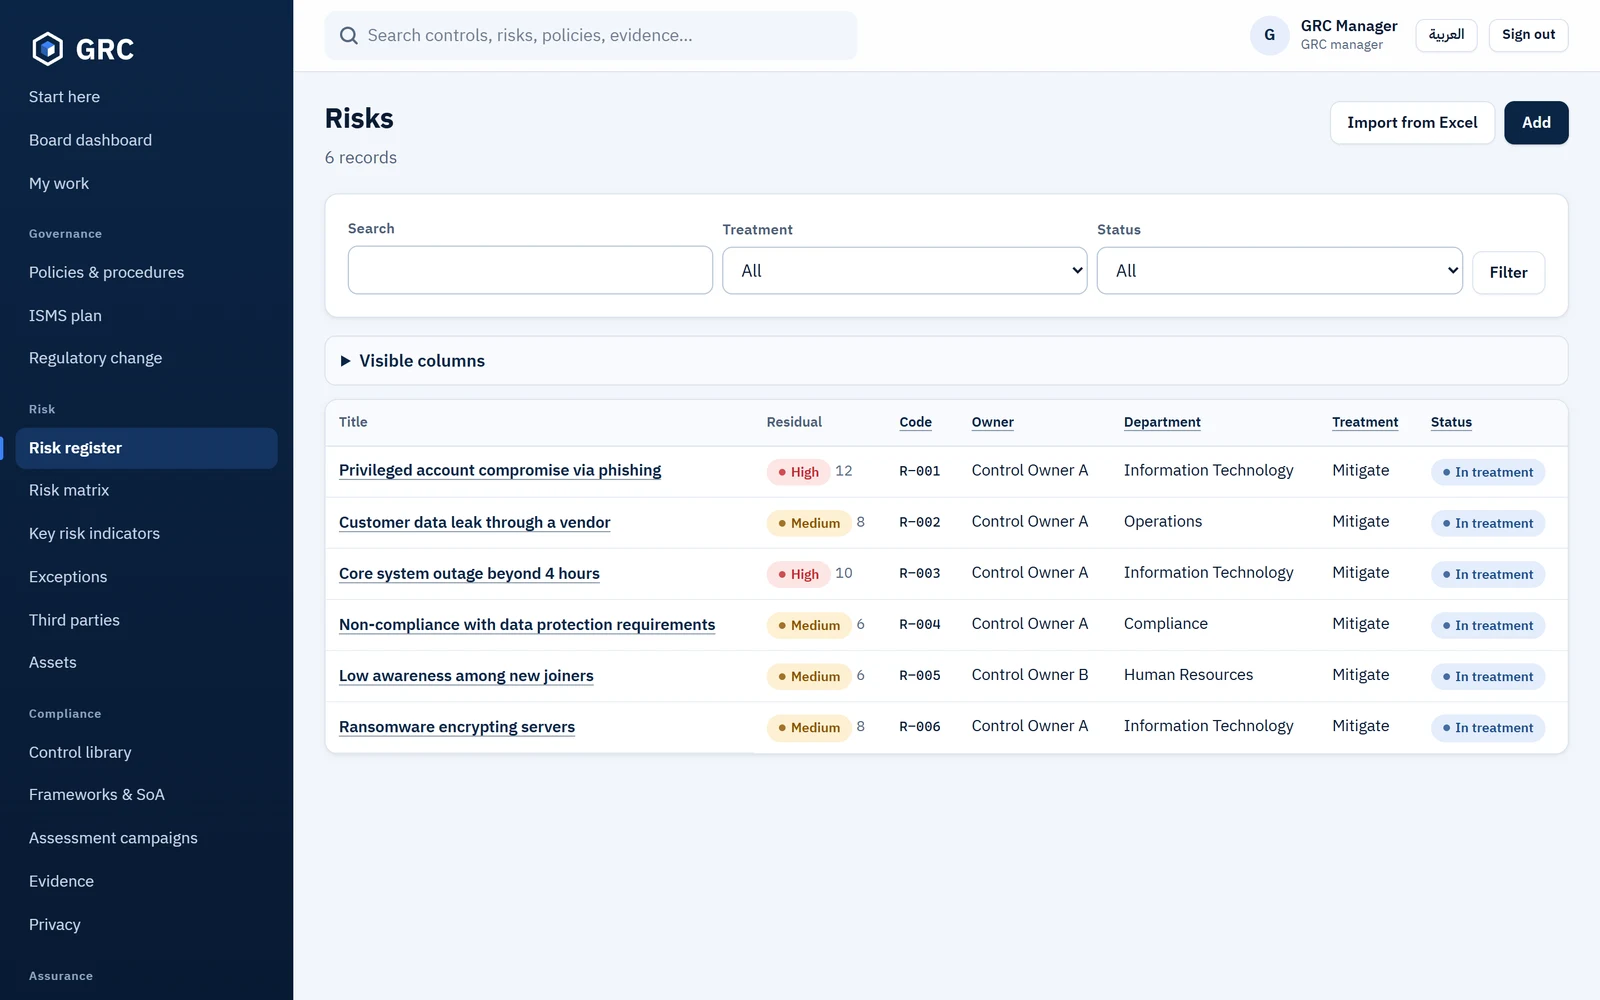
Top risks, compliance scores and open findings with their trend, so the board report is ready at any time.
Fully bilingual
Arabic and English throughout, with Word and PDF reports in your regulator's language.
From your phone
Notifications by email and Teams, with approvals and evidence uploads from a phone.
Suggests, never approves
AI suggests mappings and drafts, and approval is always made by a person.
Isolated, encrypted data
Each organisation's data is isolated from every other, and every piece of evidence is encrypted.
Why GRC
- Fully bilingual, with regulator reports in Arabic and English.
- ISO 27001 and NIST CSF 2.0 in a single control library.
- Part of one family with Inocula for awareness and DFX Index for maturity.
How to start
A live demo
We show you GRC on sample data.
A sample of your controls
We sign a non-disclosure agreement with you, then you send us a sample of your controls spreadsheet.
Your compliance map
We show you your compliance map for one framework before you decide.
Questions
Does GRC need Inocula?
No, it works on its own. With Inocula, awareness evidence arrives automatically.
Where are the ISO texts?
We keep the clause numbers and titles, and your organisation can upload its licensed text if it wishes.
Does AI approve anything?
No. It suggests mappings and drafts, and approval is always made by a person.
Is our data isolated?
Yes. Each organisation is isolated within the shared database, and every piece of evidence is encrypted.
Which languages does it support?
Arabic and English, both complete, with reports in Word and PDF.
More from this family
See where your compliance stands before you decide
We show you GRC on sample data, then use a sample of your controls to build your compliance map for one framework.
Book a demo